Penetration tests (security assessments) are controlled attacks on the resources of an organization or its individual components. Penetration testing is a form of ethical hacking — an intentional attempt of simulated cyberattacks performed by penetration testers using strategies and specialized tools to access or exploit computer systems, networks, websites and applications. Pentests reveal the actual level of information security and identify the risks that may be effectively exploited.
SC2labs offers professional penetration testing of any of the company's IT infrastructure. Depending on your needs we offer:
- Web application and API penetration tests
- Mobile application penetration tests
- PCI Penetration tests
- Internal and External Penetration service
- Black-box — zero-knowledge testing
- Gray-box — partial knowledge of the test system
- White-box — full knowledge of the test system
Focused on vulnerability/bug discovery that might be exploited via web application or API functionalities, supported business models and information flows. We use industry-proven methodologies like OWASP ASVS and NIST SP 800-95.
To deliver the assessment, testers combine dynamic testing and manual analysis: manual (dynamic) security analysis; automated (dynamic) security analysis; and automated static code security analysis (JavaScript / client side).
Software security inspections where testers manually review whether security requirements are met — security functionalities, architecture, device-server communications/data flows, authentication and authorization mechanisms, and protection of data generated and stored by the mobile application.
Business-logic checks look for misuse scenarios such as user impersonation, elevation of privileges, privacy breaches, unauthorized access, critical parameter manipulation, business constraint exploitation and unauthorized URL access.
A PCI pentest has specific requirements under PCI DSS to verify the protection of cardholder data, assessing network infrastructure and applications from both outside and inside the network environment.
PCI DSS Requirements 11.4.1 and 11.4.2 require internal and external penetration testing at least annually and after any significant change; requirement 11.4.5 requires testing of network segmentation controls. Testing covers the complete cardholder data environment (CDE) and any systems that may impact its security.
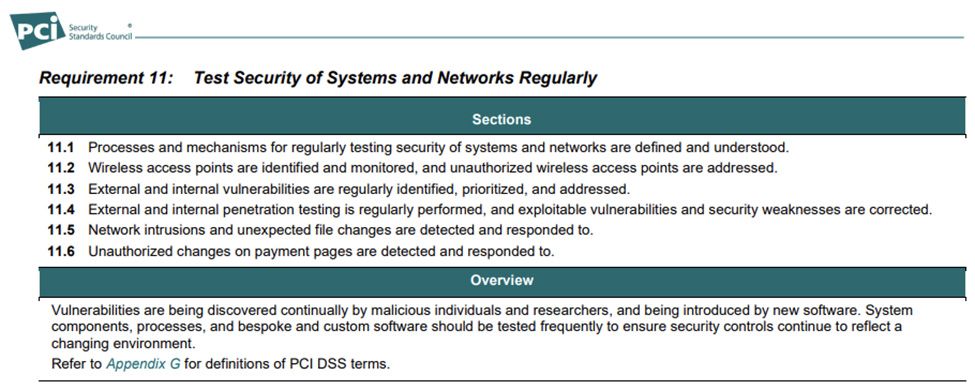
Auditors using manual and semi-automated tools evaluate the security posture of the tested network with a proven methodology to potentially compromise servers, endpoints, web applications, optionally wireless networks and other points of exposure — with minimal risk of service interruption.
External testing is conducted from outside the security perimeter (usually the Internet), beginning with reconnaissance and enumeration. Internal testing is performed remotely over VPN, assuming the identity of a trusted insider, preferably using a Kali Linux virtual machine placed in the tested network. Cloud platforms such as AWS, Microsoft Azure and Google Cloud Platform are included.
We use mainstream, industry-accepted standards and methodologies including NIST 800-115, the OWASP Web Security Testing Guide, OWASP ASVS, OWASP MASVS and the Open Source Security Testing Methodology Manual (OSSTMM).
A typical test scenario: preliminary analysis of the test system; testing and vulnerability analysis; verification of vulnerabilities via controlled attacks; risk-effectiveness assessment; and a detailed report of the results.
Our penetration testing team consists of senior members (10–15+ years of experience) holding widely recognized certificates such as CISSP, CEH, OSCP, OSCE and OSEE, with a proven track record across banking, government, payment processors, cryptocurrency exchanges and online gaming. Penetration testers are organizationally separate from the management of the tested systems and from the Qualified Security Assessors, ensuring independent results.